

SAP SoD programs that pass certification reviews and still produce audit findings. Here is the structural reason why.
The manufacturing compliance team ran the access certification campaign on schedule. Reviewers completed their attestations. The SAP SoD analysis ran clean. The records were documented.
Then the audit produced a finding.
Not because the SoD program failed to detect a conflict within SAP. Because the auditor's scope extended beyond SAP and the governance program's scope did not.
This pattern appears consistently enough in manufacturing audit findings that it is worth naming directly: most manufacturing SoD programs are configured to cover the right risks inside SAP and are structurally unprepared for the audit that tests what sits around SAP.
The configured scope problem
SAP GRC detects conflicts within the SAP role model. It does this well when rule sets are properly configured, and configuring them well is genuinely difficult work that deserves credit when it is done right.
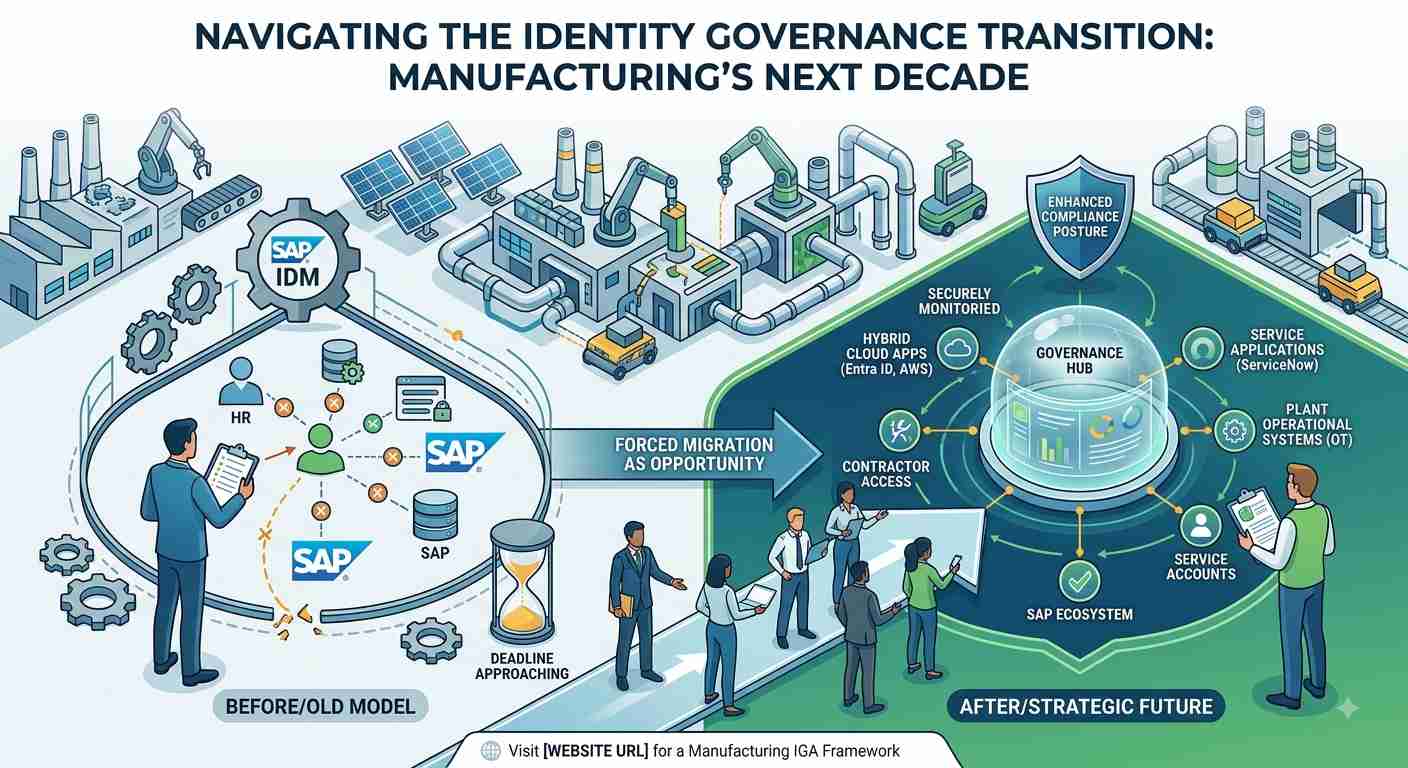
What SAP GRC does not do is analyse whether the same user who holds a standard SAP Accounts Payable role also holds administrative access to the HR system that feeds salary data into payroll. It does not evaluate Active Directory or Entra ID group memberships that determine what those users can access across the enterprise. It does not govern the contractor whose SAP access was provisioned ad hoc six months ago and whose project ended three months ago.
The configured scope and the actual risk scope diverge in most manufacturing environments. The audit finds the gap between them.
The evidence problem underneath the detection problem
There is a second issue that is less often discussed and more consistently responsible for the finding.
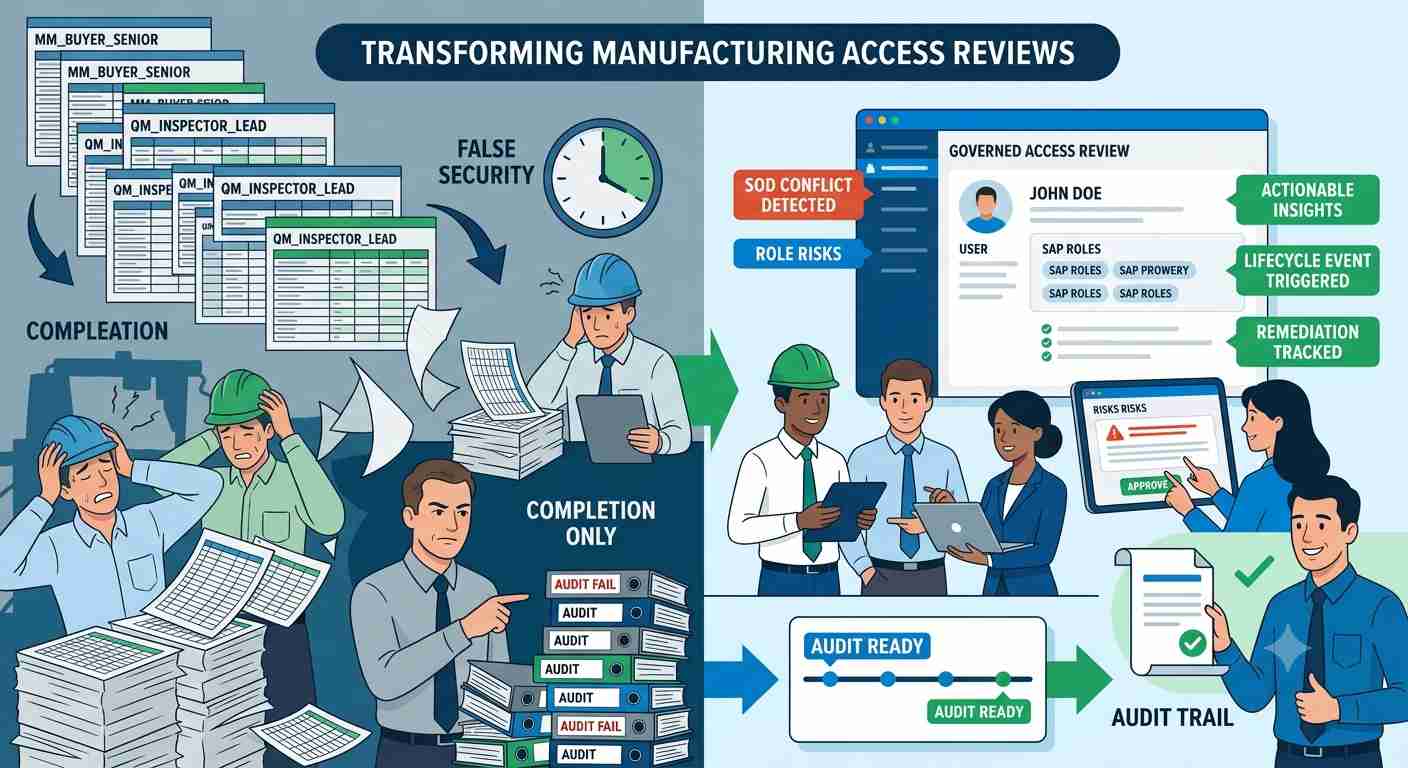
Manufacturing companies have access data. SAP exports, Active Directory logs, HR records, ServiceNow tickets. The data that would answer an auditor's questions exists across many systems.
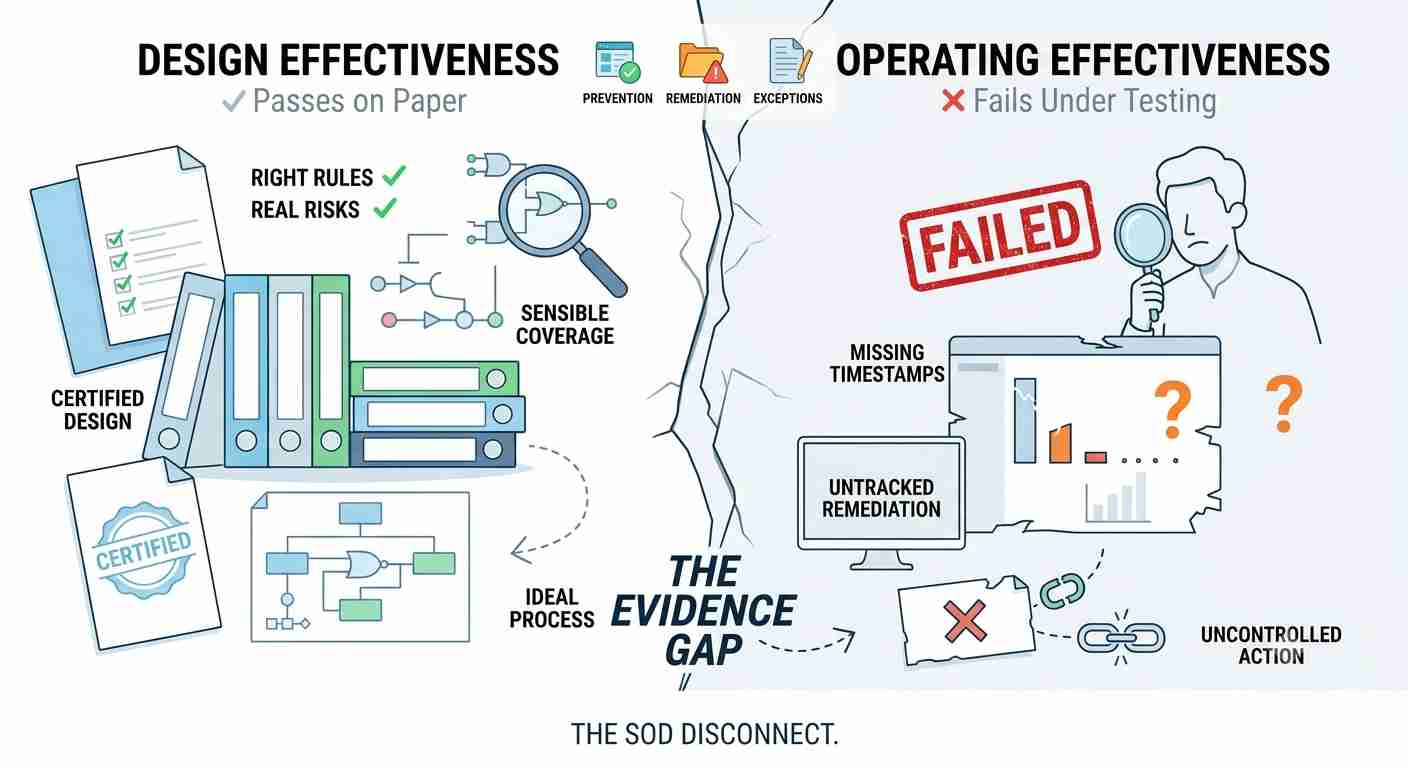
What most manufacturing companies do not have is audit-ready access evidence: a governance record that connects the access to the risk, the risk to the reviewer, the reviewer to the decision, and the decision to the remediation, in a format that does not require manual reconstruction at the point an auditor asks for it.
When the answer to "why did this user hold this access combination" requires correlating an SAP export, a spreadsheet from the last certification campaign, an email thread, and a ServiceNow ticket, the finding is generated not by the conflict but by the inability to demonstrate what happened after the conflict was identified.
Manufacturing does not have an access-data problem. It has an access-evidence problem.
The five questions that separate a mature program from a documented risk
When a conflict surfaces during an audit, five questions determine whether it becomes a reportable deficiency or a documented exception.
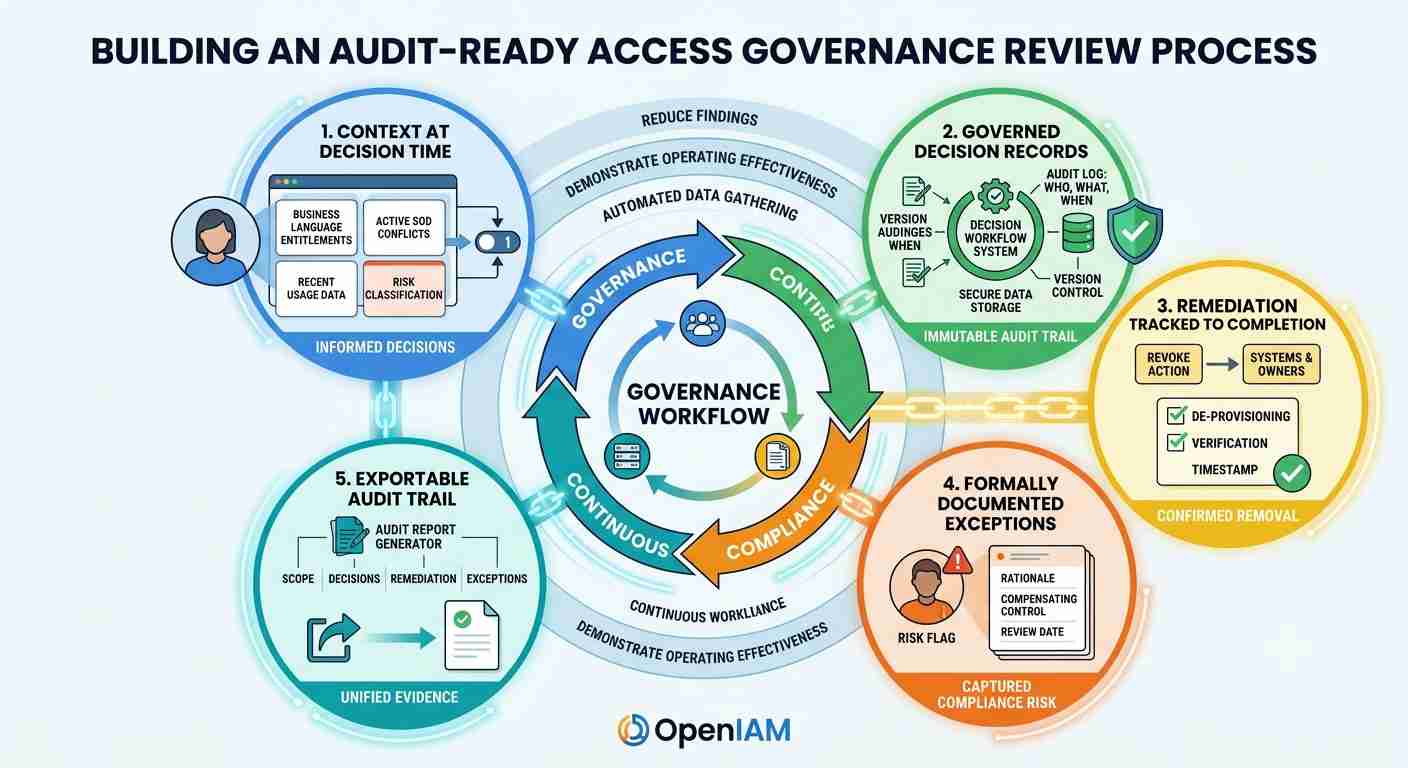
What access did this user hold, and when? Was this access flagged as a risk, at the transaction code level, mapped to a control objective? Who reviewed it, and when? What was decided, whether remediation or accepted risk with a compensating control? What happened after the decision, and is the evidence of that outcome timestamped and retrievable?
A program that can answer all five, across SAP and every connected system, does not eliminate audit findings. It changes what the auditor finds from a governance architecture problem to individual exceptions. That is a fundamentally different conversation to have in the audit room.
What the scope expansion actually requires
Closing the gap requires three disciplines operating simultaneously. Preventive controls that evaluate SoD risk before conflicting access is assigned. Detective controls that scan continuously across all connected systems and not just within SAP on a quarterly schedule. And evidence that connects both disciplines to a single retrievable governance record showing what was found, who reviewed it, what was decided, and what action was taken.
None of these three requires replacing an existing SAP GRC investment. They require extending the governance perimeter beyond the SAP boundary that the existing investment was designed to cover.
The audit was never just SAP. The governance program needs to reflect that.
What is the most common SoD audit finding manufacturing compliance teams are encountering right now? The experiences of teams working through this would be worth hearing.